How to Tell if Your WordPress Site Is Hacked: Warning Signs, Quick Checks and What to Do First
How to tell if your WordPress site is hacked: redirects, spam pages in Google, unknown admins and warnings, a quick checklist and the first steps to take.

On this page
- Warning signs that your WordPress site has been hacked
- How to know if your WordPress site has been hacked: 10 quick checks
- How to check if a WordPress site is hacked without logging in
- How to check a WordPress site for hacks with WP-CLI or SSH
- Hacked or just broken? Common false alarms
- What to do first if your WordPress site has been hacked
- How to stop it happening again
- How to check if a WordPress store or payment page is hacked
- A monthly hack check you can do in 15 minutes
- FAQs
- When to get help
- A hack usually shows up in one of four places: what visitors see, what Google shows, what the WordPress admin shows and what the server shows.
- To check if a WordPress site is hacked, run a site: search, open the Search Console Security Issues report, review admin users and scan files, then visit as a stranger on mobile data.
- If you find a problem, back up the infected copy, change every password, clean core, plugins and database, hunt for backdoors and close the entry point before asking Google for a review.
You can tell your WordPress site has been hacked if visitors are redirected to spam or scam sites, Google shows pages you never created (often Japanese or pharma keywords), there are admin users you did not add, or Chrome or Google shows "Deceptive site ahead" or "This site may be hacked". To check for sure, search site:yourdomain.com in Google, open Security Issues in Search Console, review your administrator accounts and scan the files.
Short answer: To check if your WordPress site is hacked, search site:yourdomain.com for pages you never made, open your site logged out on a phone from a Google result to catch redirects, read Security Issues in Search Console, and look for admin users, plugins or PHP files you did not add. Two or more hits means it is almost certainly hacked.
Quick checklist:
- Search
site:yourdomain.comin Google and look for pages you never created. - Open your site on a phone, logged out, from a Google result, and watch for redirects.
- Check Security Issues and Manual Actions in Search Console.
- Review Users and remove administrator accounts you did not add.
- Look for plugins, themes or files you did not install, and run a malware scan.
- If any check fails, change every password, take a backup and start the clean-up steps below.
If you would rather not do this yourself, WordPress maintenance and security support covers clean-ups and hardening.
Warning signs that your WordPress site has been hacked
One sign on its own can have an innocent cause; two or more together means investigate properly.
| Symptom | How to check | What it usually means |
|---|---|---|
| Visitors redirected to gambling, dating or scam pages | Open the site logged out, on mobile data, from a Google result | Redirect hack; often skips logged-in admins |
| Japanese, pharma or replica pages in Google | Search site:yourdomain.com | Japanese keyword SEO spam hack |
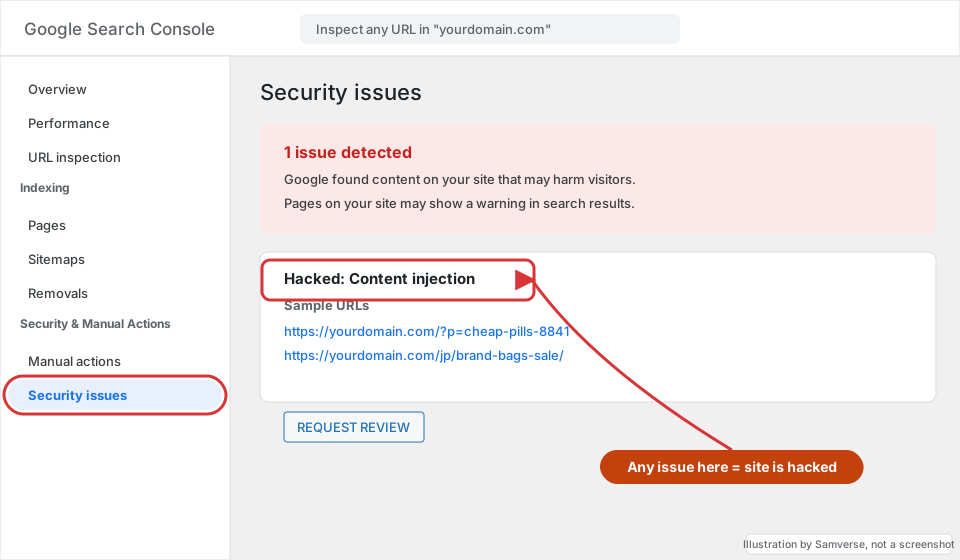
| "Deceptive site ahead" or "This site may be hacked" | Search Console, Security Issues; Google Safe Browsing site status | Google has detected malware or phishing; see fixing "Deceptive site ahead" |
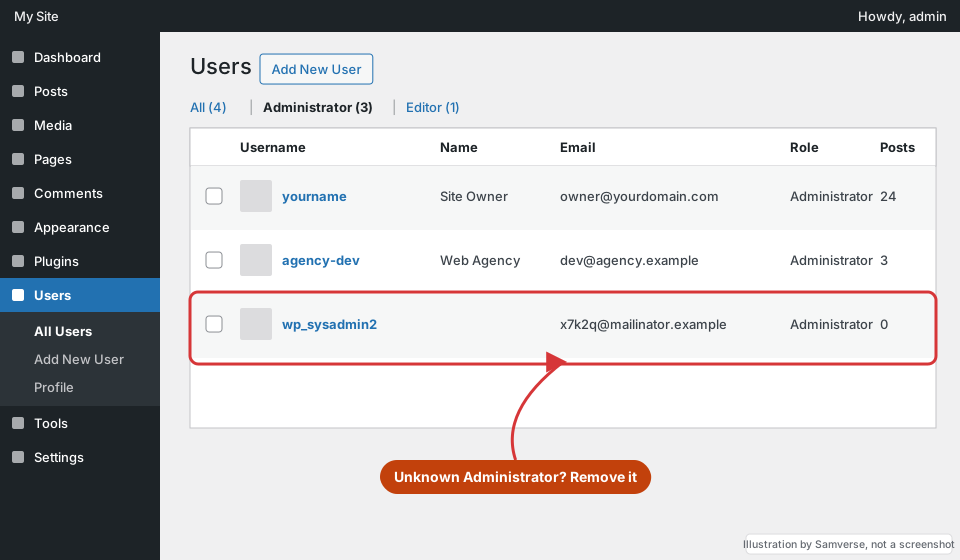
| Admin users you did not create | Users, filter by Administrator | Attacker access; assume a backdoor too |
| Unknown plugins or PHP files in uploads | Plugins list; wp-content/uploads in File Manager | Malware or a backdoor |
| Host suspension or malware email | Hosting inbox and panel notices | The host's scanner found infected files |
| Spam bounces or mail limits | Mail logs, bounce messages | Your server is sending spam |
| Sudden slowness or high CPU | Hosting resource graphs | Hidden scripts mining, spamming or attacking other sites |
| New footer links, injected text or defacement | View page source, logged out | Database or theme files changed |
| Password stops working, reset email never arrives | Hosting database tool or WP-CLI user list | Admin email changed by the attacker |
Related: a WordPress activity log and stopping spam user registrations in WordPress.
How to know if your WordPress site has been hacked: 10 quick checks
Work through these in order. Most take a few minutes.
- Run a site: search. Search site:yourdomain.com and look for titles, languages or URLs you do not recognise.
- Open Search Console Security Issues. In Google Search Console, open Security and Manual Actions, then Security Issues. Google lists detected malware, hacked content and deceptive pages here.
- Check Search Console pages and sitemaps. A sudden jump in indexed pages, or sitemaps you did not submit, points to injected spam.
- Visit the site as a stranger. Use a private window on your phone with mobile data, and click through from a Google result. Many redirect hacks only trigger this way.
- Review your users. In Users, filter by Administrator. Delete or demote anyone you cannot identify, and check the email address on your own account.
- Review plugins and themes. Look for plugins you did not install, or anything nulled. Read why nulled themes and plugins are risky.
- Look at recently modified files. In your hosting file manager or over SFTP, sort folders by modified date. PHP files changed on a day nobody worked on the site, or any PHP file in wp-content/uploads, need a closer look.
- Check key files. Open .htaccess, wp-config.php and index.php. Long lines of encoded text, eval, base64_decode or unfamiliar redirect rules are red flags.
- Run a malware scanner. Use a security plugin scan and an external scanner; a clean result is reassurance, not proof. Our malware scanner comparison explains the differences.
- Check the database. Search the wp_options and wp_posts tables for script tags, iframes or unfamiliar domains, especially in siteurl, home and widget settings.
How to check if a WordPress site is hacked without logging in
If you cannot log in, checks 1, 2 and 4 above still work from outside. Also:
- Use Google Safe Browsing's site status page to see if the domain is flagged.
- View the page source and search for unfamiliar script sources or iframes pointing to other domains.
- Run an external website scanner, which checks the public pages for known malware and blacklist status.
External checks only see public pages; a quiet backdoor needs file and database access to find.
How to check a WordPress site for hacks with WP-CLI or SSH
With SSH access, these commands are faster than a file manager. Run them from the WordPress folder:
wp core verify-checksumscompares every WordPress core file with the official copy and lists anything changed or added. A clean core prints "Success".wp plugin verify-checksums --alldoes the same for plugins from wordpress.org (premium plugins will show as unverifiable, which is normal).wp user list --role=administratorlists every admin with their email and registration date.find wp-content/uploads -name "*.php"should return nothing on most sites. A PHP file in uploads is almost always malicious.find . -name "*.php" -mtime -7lists PHP files changed in the last seven days. Compare it with the dates you actually updated anything.grep -rl "eval(base64_decode" wp-contentfinds the most common pattern used to hide injected code. Legitimate plugins rarely use it.wp db search "<script" wp_options wp_postsfinds script tags injected into settings and content.
Also look for a wp-content/mu-plugins folder you did not create. Must-use plugins load automatically and do not appear in the normal Plugins list, which makes them a favourite hiding place.
Hacked or just broken? Common false alarms
Not every problem is a hack. Rule out these first:
| Symptom | Possible innocent cause | What points to a hack |
|---|---|---|
| Site is slow | Heavy plugins, cheap hosting, large images | High CPU at odd hours, unknown processes, outgoing spam |
| Redirect loop | SSL or URL settings mismatch | Redirects to unrelated external domains |
| White screen | Plugin or PHP version conflict | Modified core files, encoded code in index.php |
| Can't log in | Forgotten password, security plugin lockout | Admin email changed, unknown admins |
| Traffic drop | Algorithm update, tracking broken | Spam pages indexed, security warning in Search Console |
If you are not sure, see fixing too many redirects or why website traffic drops to rule out the non-security causes.
What to do first if your WordPress site has been hacked
The order matters: rushing to delete things destroys the evidence of how attackers got in.
- Do not panic-delete. Back up of files and database as they are now, labelled as infected.
- Change every password. WordPress admins, hosting panel, SFTP, database and the email account linked to the admin. Update the security keys in wp-config.php so every session is logged out.
- Put the site in maintenance mode if visitors are at risk, for example when it redirects to scams or the checkout is affected.
- Clean properly. Replace WordPress core with a fresh copy, reinstall plugins and themes from official sources, remove unknown files and clean injected database content. Our step-by-step malware removal guide covers this.
- Hunt for backdoors. Attackers usually leave a way back in. See finding and removing WordPress backdoors.
- Find and close the entry point. Usually an outdated plugin, a weak or reused password, a nulled theme or another infected site on the same hosting account.
- Request a review. Once clean, request a review in Search Console so Google removes the warning, then follow our guide to recovering rankings after a hack.
How to stop it happening again
Most hacks come from a short list of causes (see why WordPress sites get hacked). These habits prevent most of them:
- Keep WordPress, plugins and themes updated, and remove anything you do not use.
- Use strong unique passwords and two-factor authentication for every admin.
- Give each person their own account with the lowest role they need.
- Avoid nulled themes and plugins completely.
- Keep automatic off-site backups, and test that they restore.
- Use a firewall and monitoring so you hear about problems before your customers do.
Our full WordPress security checklist goes through each step.
How to check if a WordPress store or payment page is hacked
Attackers in a WooCommerce site often target money, and the shop keeps working while payments or customer data are quietly diverted. Check:
- Checkout scripts: view the source of the checkout page and look for scripts loading from domains you do not recognise. Card and payment skimmers sit here. See WooCommerce checkout skimmer malware.
- Payment settings: open each payment gateway's settings and confirm the account details, API keys and any UPI ID shown to customers are still yours.
- Contact details: check that the phone number, WhatsApp link and bank details on the contact page, order emails and invoice templates have not been changed.
- Orders and customers: look for unusual admin-created orders, coupons you did not create, or new shop manager accounts.
- Emails: place a test order and check the email for added links.
If anything looks wrong, put the checkout into maintenance mode, tell your payment provider and clean up before taking orders again.
A monthly hack check you can do in 15 minutes
Repeat checks 1, 2, 4, 5 and 6 from the list above once a month, and confirm your latest off-site backup exists and restores (see the WordPress backup and restore guide). A WordPress maintenance plan can include this routine if you would rather not do it yourself.
FAQs
How do I check if my WordPress site is hacked?
Run a site: search for spam pages, open the site logged out from a Google result on a phone, check Security Issues in Search Console, review administrator accounts and recently modified files, and run a malware scan. If two or more checks fail, treat the site as hacked.
How do I tell if my WordPress site has been hacked?
Redirects to unrelated sites, spam pages in a site: search, unknown admins, Google or browser warnings and unexpected file changes. Confirm with Search Console and a malware scan.
How can I check if my WordPress site is hacked for free?
A site: search, the Search Console Security Issues report, Google Safe Browsing site status, a free security plugin scan and a review of your users and recently modified files are all free and cover most common hacks.
Why can't I see the hack when I visit my own site?
Many hacks hide from logged-in users and only trigger for visitors arriving from Google, often on mobile. Test in a private window on mobile data from a search result.
Can a malware scanner tell me my site is definitely clean?
No. Scanners catch known patterns; well-hidden code can slip through, so combine a scan with file, user and database checks.
Will my Google rankings recover after a hack?
Usually, once the spam pages are removed, the site is cleaned and Google's warning is lifted. How quickly depends on how long the hack ran and how many spam pages were indexed.
Should I fix a hacked WordPress site myself or hire someone?
If you are comfortable with SFTP, databases and file comparison, you can follow a careful process. If the site handles payments or enquiries, or the hack keeps coming back, professional help is usually quicker and safer.
When to get help
Get help quickly if the site takes payments, Google is already showing a warning, you cannot find the entry point, or the hack comes back after a clean-up. If your checks point to a hack, Samverse offers hacked WordPress site repair and security, including clean-up, backdoor removal and getting Google warnings lifted. For ongoing protection, see WordPress maintenance and support, or hire a WordPress developer in India for a one-off security review.
Need help with your website?
I'm a freelance WordPress developer building fast, SEO-friendly websites since 2020. Tell me what you need and I'll reply with a plan and a fixed quote, usually within 24 hours.
Freelance WordPress development, building websites for clinics, manufacturers, agencies and online stores since 2020.
More about me